~/blog
Kerim Tarik

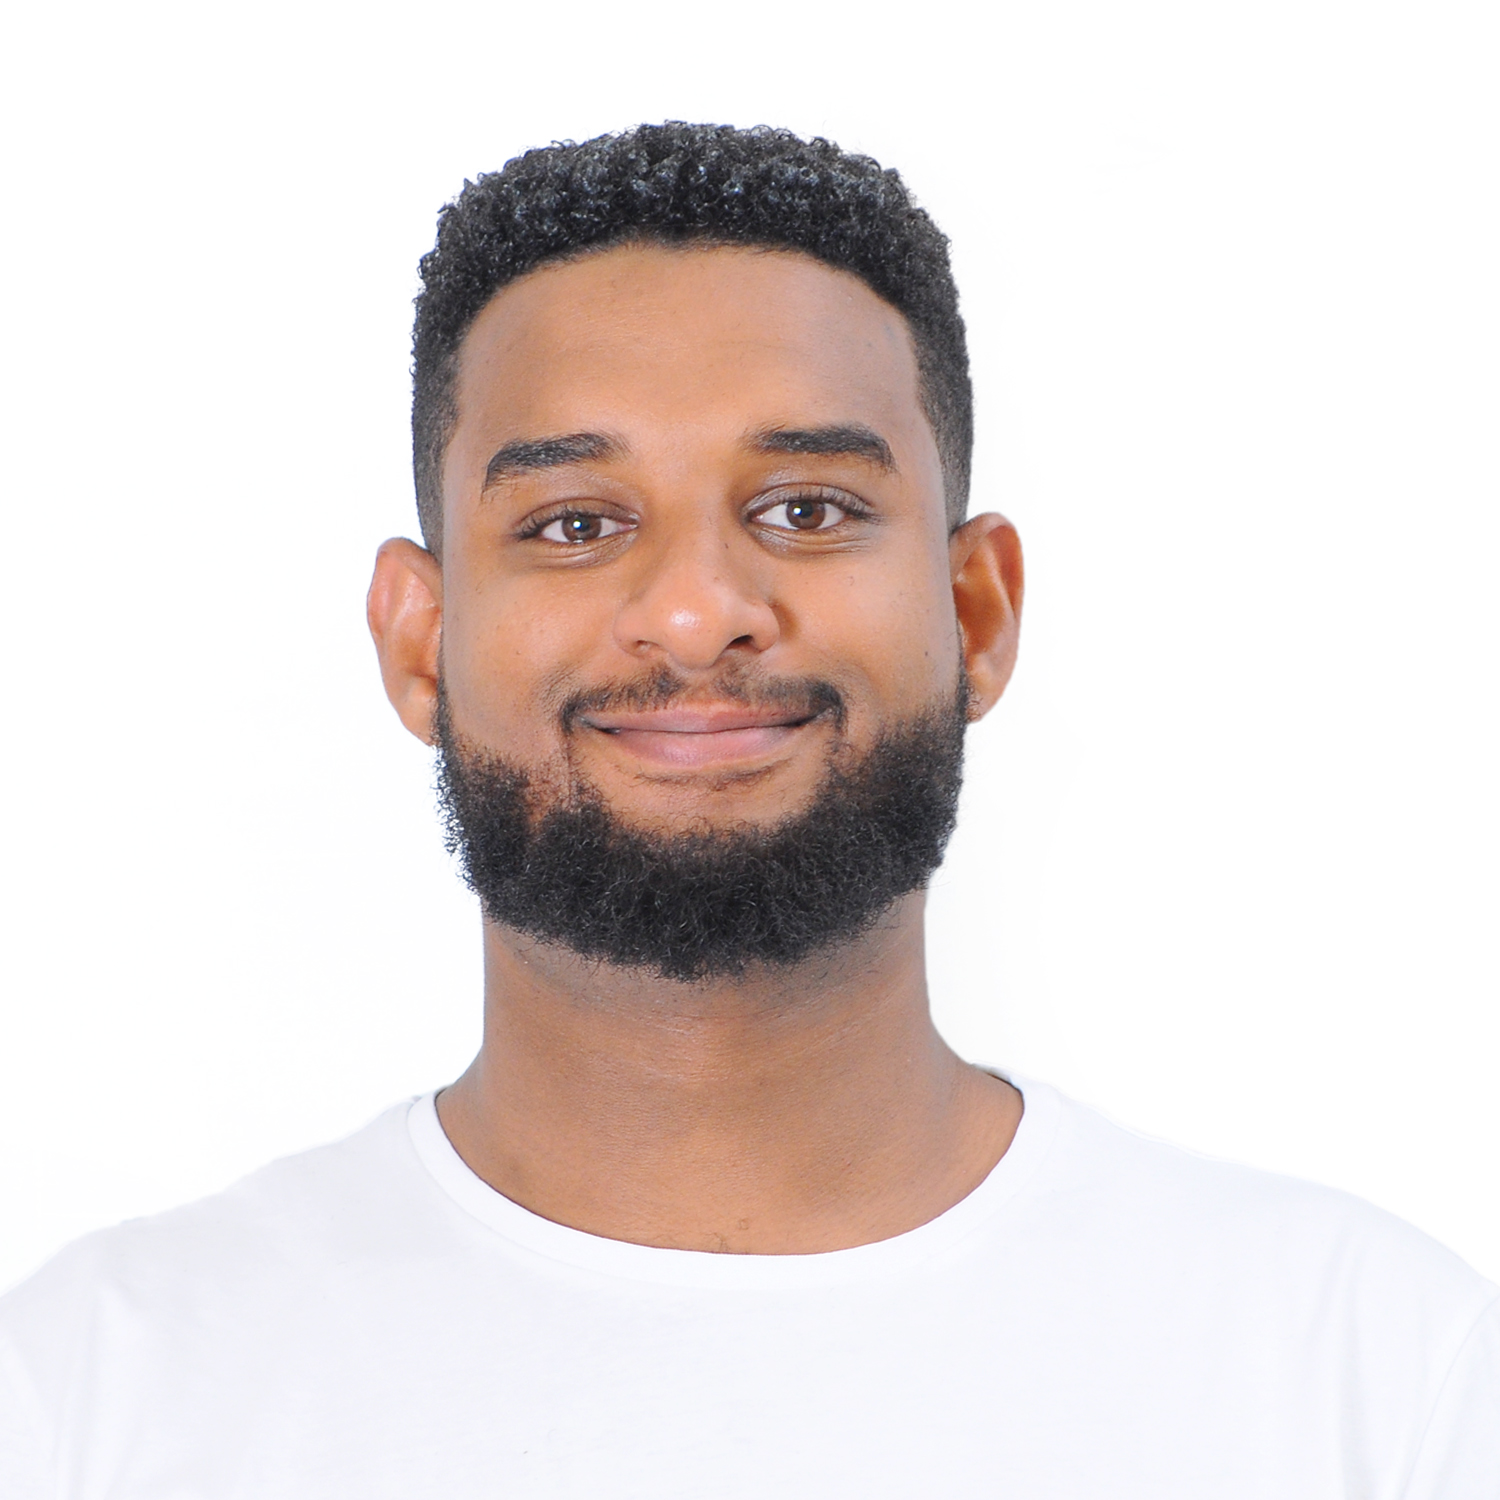
Hi, I'm Kerim

Scroll Down

  • Addis Ababa, Ethiopia
  • 4 years in tech, now focused on offensive security
  • Penetration Tester · OSCP · HTB CPTS

I'm a penetration tester based in Addis Ababa, holding the OffSec OSCP and the Hack The Box CPTS. I find and exploit weaknesses in networks, web applications and Active Directory environments before real attackers do, then turn the results into clear reports and practical fixes. My background building full-stack software means I understand the systems I test from the inside.

Portofolio

Skills & Tools

  • Kali Linux
  • Burp Suite
  • Metasploit
  • Nmap
  • Active Directory
  • Wireshark
  • Python
  • Bash
  • PowerShell
  • Linux
  • Hack The Box
  • OWASP

Services

  • External & internal network penetration testing
  • Web application testing against the OWASP Top 10
  • Active Directory attack-path assessments
  • Clear pentest reports with prioritised remediation

OSCP

OffSec Certified Professional

CPTS

HTB Certified Penetration Testing Specialist

Web · Net · AD

Assessment Coverage

Experience, Education & Certifications

  1. 2025

    OSCP — Offensive Security Certified Professional

    OffSec's hands-on penetration testing certification: a 24-hour exam compromising Linux, Windows and Active Directory targets, followed by a professional report.

  2. 2025

    HTB CPTS — Certified Penetration Testing Specialist

    Hack The Box's intermediate-to-advanced pentest certification: a multi-day, real-world engagement against an enterprise network and Active Directory, delivered as a commercial-grade report.

  3. August 2024

    IELTS Certification

    Achieved an overall score of 8 on the IELTS English proficiency test.

Projects

$ nmap -sC -sV -p- 10.129.0.0/24

[+] 14 hosts up, 87 open ports

$ ligolo-ng -selfcert

[+] tunnel established -> 172.16.8.0/23

$ secretsdump.py -just-dc corp.local/admin@dc01

[+] krbtgt hash dumped — domain compromised

$ ▌

Certification Engagement

2025

HTB CPTS Exam — Full Network Compromise

Completed the Hack The Box Certified Penetration Testing Specialist exam: a multi-day, black-box engagement against an enterprise network, from external recon to full Active Directory domain compromise, delivered as a commercial-grade penetration test report.

  • Active Directory
  • Pivoting
  • Web Exploitation
  • Privilege Escalation
  • Reporting

$ autorecon 192.168.x.x

[+] 445/tcp smb 80/tcp http 3389/tcp rdp

$ python3 exploit.py --lhost tun0

[+] reverse shell as iis apppool

$ whoami

nt authority\system

$ ▌

Certification Engagement

2025

OSCP — Offensive Security Certified Professional

Passed the OffSec OSCP: a 24-hour hands-on exam covering standalone Linux and Windows targets and an Active Directory set, followed by a professional exploitation report with full reproduction steps.

  • Enumeration
  • Exploit Development
  • Linux
  • Windows
  • Active Directory

$ cat user.txt

[+] user flag captured

$ sudo -l

(root) NOPASSWD: /usr/bin/tar

$ cat /root/root.txt

[+] root flag captured

$ ▌

Labs & Research

Ongoing

Hack The Box Labs & Writeups

Rooted machines and Pro Lab environments on Hack The Box, documenting the attack path for each: enumeration, initial foothold, lateral movement and privilege escalation, along with defensive takeaways.

  • Hack The Box
  • Linux PrivEsc
  • Windows PrivEsc
  • Kerberos Attacks
  • Writeups

Get In Touch

Need a penetration test, an Active Directory assessment, or a second set of eyes on your web application? Get in touch to discuss scope and rules of engagement. All testing is carried out only with written authorization.

Send me a message